


Strategy
In security history, defenders once relied on a time gap—averaging two and a half years from vulnerability disclosure to weaponized exploitation, but by 2026 this has shrunk to hours, with the frontier model Mythos as the primary cause. This brings a dual challenge: unknown attacks (zero-day vulnerabilities with no CVE to look up) and a flood of known vulnerabilities (report overload causing prioritization chaos). Static code scanning cannot solve either problem; only runtime execution-based monitoring, which observes code and agent behavior in real time, can block unknown threats without relying on CVEs and filter out truly exploitable vulnerabilities, turning prioritization from guesswork into precision.
The latest Government Accountability Office (GAO) report indicates that approximately 70% of federal cybersecurity regulations contain redundant reporting requirements. Among 117 rules issued by 37 agencies, 80 cover the same areas, involving 125 distinct requirements. The report warns that without regulatory coordination, the CIRCIA rule will exacerbate compliance burdens for industries such as finance.
Black Kite's report indicates that 43% of victim organizations still have at least one unpatched critical vulnerability, 31% have vulnerabilities known to be exploited by CISA, 59% have incorrectly configured DMARC, and 32% have misconfigured DKIM records. Attackers use AI to enhance their attack capabilities, and manufacturing has been the most victimized industry for four consecutive years.
AI agents are shifting from code assistance to directly operating production systems, making MCP servers the new security boundary. However, many organizations still rely on static credentials and overly broad permissions, overlooking the credential risks behind AI interactions. This article analyzes how MCP changes the infrastructure security model, the new pathways for secret leakage introduced by AI workflows, and proposes governance practices such as treating AI agents as privileged identities and adopting dynamic credentials and least privilege.
The U.S. Government Accountability Office (GAO) released an audit report indicating major flaws in the cybersecurity protection of the U.S. aviation system: the FAA has only partially implemented cybersecurity strategic goals, and the TSA has failed to clearly define its cybersecurity responsibilities. The report recommends that relevant agencies accelerate corrective actions and sets a specific timeline.
Recorded Future released a report on Thursday revealing that Iran-linked actors are integrating artificial intelligence into cyber and information warfare, covering areas such as malicious software development and reconnaissance of industrial control systems. While there are no signs of fully autonomous models, AI has significantly shortened the distance from intent to action. The report cites specific cases involving groups such as MuddyWater and Ababil of Minab, and notes that Iran collaborates with China and Russia to compensate for its own limitations.
The Trump administration announced on Tuesday the launch of the Gold Eagle project, aimed at coordinating the use of cutting-edge AI models in vulnerability discovery and remediation to address the surge in vulnerabilities caused by AI. The project will collaborate with Carnegie Mellon University, utilize the VINCE platform, and focus on open-source software, but faces challenges such as coordination with existing industry projects and legal authorization deadlines.
A report released by the SANS Institute on July 13 indicates that the adoption rate of AI among enterprise security teams has jumped from 50% to 78% within a year, but governance policies lag significantly behind. 40% of security practitioners report that their organizations lack a formal AI adoption policy, and over 60% are unable to track AI model usage and data exposure risks. Report author Matt Bromiley points out a 14-percentage-point perception gap between security leaders and frontline practitioners, highlighting the practical challenges in governance implementation.
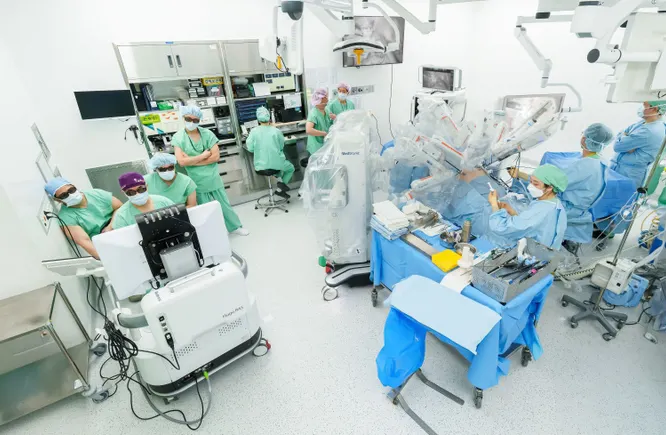
Cybersecurity firm Fortified Health Security released a mid-year report indicating that the healthcare industry is being overwhelmed by growing cyber threats, with the risk remediation rate dropping sharply from 23% in the same period last year to 6% in the first half of 2026, making supply chain security and identity management two major persistent problems.
In security investigations, analysts often switch between multiple tools to piece together the truth about attacker infrastructure, but attackers' automation and AI have lowered the cost of scaling, causing infrastructure to change far faster than traditional intelligence pipelines. This article argues that security teams should ask the internet itself directly, integrating external context into security operations through real-time data, APIs, and AI workflows to keep pace with the accelerating threat tempo.