


Deep Dive
来自我们记者的行业洞察
AWS dominates the cloud market, but its voice in the cybersecurity community is not as prominent as that of Microsoft and Google. Although AWS is not inferior in security capabilities, its shared responsibility model and customer-centric approach to information disclosure make it appear conservative in security thought leadership. Multiple analysts point out that this low-key stance may stem from business strategy rather than insufficient security investment.
CommonSpirit Health suffered a ransomware attack this month, drawing attention to cybersecurity risks during the integration period of healthcare industry mergers and acquisitions. Experts point out that system integration, weak supply chains, and distracted executive attention during M&A make healthcare organizations more vulnerable to attacks. The FBI has also warned that ransomware groups tend to launch attacks during major financial events.
The software bill of materials (SBOM), as a tool to enhance cybersecurity in medical devices, has entered a critical development phase driven by the Biden executive order and NTIA initiatives. The FDA plans to incorporate SBOM into premarket submission requirements and is exploring a broader cybersecurity bill of materials (CBOM). However, the industry has concerns about information leakage risks and implementation burdens, with NTIA and AdvaMed debating access control and standardization.
The COVID-19 pandemic brought Microsoft a 34% increase in commercial cloud revenue, but incidents like SolarWinds also put its security capabilities to the test. By integrating products, acquiring companies such as Rubrik, investing $20 billion to bolster security, and appointing Charlie Bell to lead a new security division, Microsoft aims to solidify its position as a provider of end-to-end security solutions in the era of remote work.
As ransomware attacks become increasingly sophisticated, one of the biggest cybersecurity challenges for healthcare organizations is defending aging medical devices against emerging cyber threats. These devices were often designed without cybersecurity in mind and run on operating systems that have reached end-of-life, making them difficult to patch.
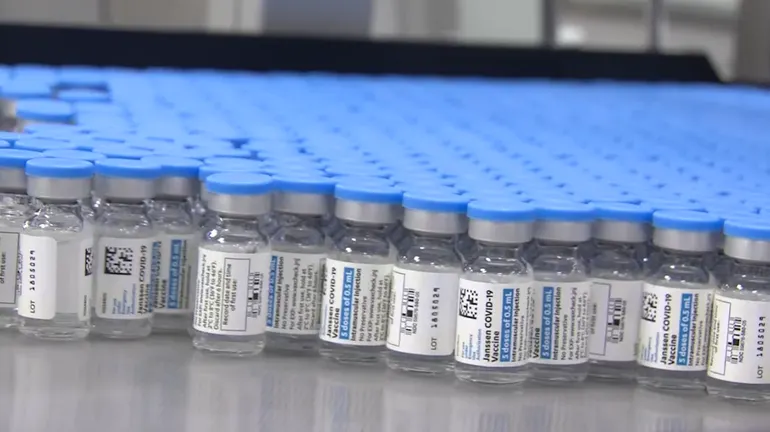
Moderna, Pfizer, and Johnson & Johnson vaccines have received FDA emergency use authorization, and AstraZeneca also plans to submit for review. The global distribution of multiple vaccines across multiple supply chains brings unprecedented complexity, also fostering cyberattack and counterfeiting risks targeting vaccine research and distribution. Industry experts point out that zero trust strategies, real-time visibility tracking, distributed ledgers, and digital authentication and serialization are four key technical tools for current risk prevention.
Ransomware has evolved from a threat targeting individuals to a serious risk capable of paralyzing large enterprises. Based on data analysis from Cybersecurity Dive, this article explores the scale, scope, and impact of ransomware attacks on businesses, and also focuses on the threats faced by small organizations.
When data breaches become inevitable, CISOs often serve as the public "scapegoat" for companies. The "golden bullet" clause, as a financial protection mechanism, can provide compensation when a CISO departs due to a security incident. Drawing on industry expert opinions and data from organizations such as Nominet and Risk Based Security, this article examines the operational logic, practical limitations, and profound impact of this clause on CISO career development.