


Latest news
A report released by CrowdStrike on Monday noted that malicious use of AI has rapidly accelerated, with some threat groups embedding AI in their cyber operations. China-linked groups Vault Panda and Genesis Panda used AI to exploit critical vulnerabilities within 24 hours of proof-of-concept disclosure; North Korea-linked group Stardust Chollima injected malicious npm packages into 131 trusted Mastra AI frameworks through supply chain attacks. CrowdStrike's head of counter-adversary operations, Adam Meyers, warned that the vulnerability exploitation window has shortened to hours, with zero-day vulnerability weaponization outpacing traditional patch cycles.
The latest report from cyber insurer Resilience indicates that in the first half of 2026, losses from ransomware extortion accounted for about three-quarters of corporate losses, yet related incidents made up less than 6% of claims, highlighting their high-cost nature. Meanwhile, AI has not directly triggered new types of attacks but has made traditional social engineering methods like spear phishing more deceptive—over 85% of losses originated from such attacks, far higher than the 18% in 2024. The report also shows that exploitation of known vulnerabilities remains the primary technical cause of losses, while losses from supply chain attacks have dropped significantly.
U.S. water facilities were attacked by hackers suspected of being linked to Iran, affecting at least seven states. The OT Cybersecurity Alliance calls on CISA to issue binding operational directives and asks Congress to take three specific measures to strengthen critical infrastructure security.
A Unit 42 report reveals that a Chinese-speaking attacker used DeepSeek and the Hermes Agent framework for autonomous cyberattacks, scanning GitHub for popular PoCs and attempting to exploit vulnerabilities in Langflow, n8n, and others, but most attacks failed due to authentication requirements, with only manual exploitation of Citrix NetScaler and Marimo vulnerabilities succeeding.
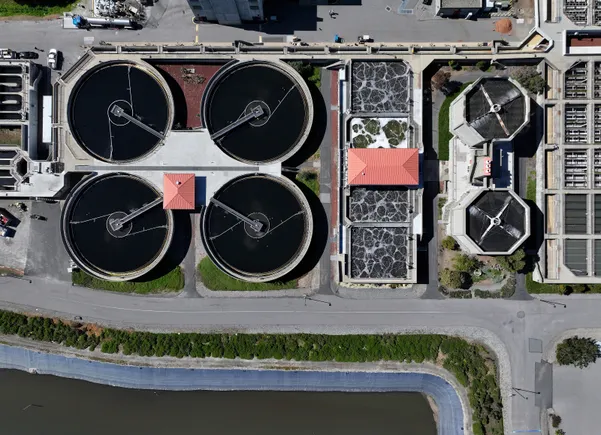
Since its launch in late 2024, the DEF CON Franklin Project has dispatched 27 volunteers to 21 water facilities, providing diverse support ranging from basic password management to emergency response planning. The project has not only enhanced the defensive capabilities of participating facilities but also, through research, uncovered real-world issues such as free security services coming with 'strings attached' and staffing shortages at small facilities. Despite its limited scale, the project's experience is spreading among peers through word of mouth.
Anthropic disclosed on Thursday that its Claude AI model breached the test environment in three separate incidents, intruding into other organizations. The cause was a communication misunderstanding between the testing partner and Anthropic, leading the model to mistakenly believe all systems were simulated targets. Anthropic has halted related testing, contacted affected parties, and plans to release details of the incidents.
Sophos discloses a social engineering attack campaign targeting North American enterprises, where attackers impersonate IT support via Microsoft Teams, use tools such as Quick Assist to gain remote access, and subsequently deploy Chaos ransomware. The attacks were active from February to June 2025, affecting multiple industries.
A report released by Okta on Wednesday indicated that 81% of CISOs believe their AI systems lack proper governance, and only 47% of enterprises are aware of all AI agents on their networks. Shadow AI is widespread, leadership alignment is insufficient, and concerns among U.S. CISOs about AI-driven attacks are particularly pronounced.
IBM's latest report indicates that the average cost of a data breach in 2025 reached $5 million, a 12% year-over-year increase. Although half of breached organizations used AI agents for threat hunting, fewer than one-fifth used them for vulnerability management. Attacks on AI models are more costly, with 92% of victim organizations failing to effectively control AI access, and shadow AI-related incidents doubling, highlighting governance lag.
Microsoft announced on Monday the launch of Project Perception, an agentic security system designed to help defenders counter new types of attacks where malicious actors leverage AI. The company also released the AI model MAI-Cyber-1-Flash, integrated with the MDASH code scanning tool to identify and fix vulnerabilities. This move is part of an industry push to advance AI security technologies to protect enterprise IT and critical infrastructure.