Deep Dive
来自我们记者的行业洞察
After losing federal funding, MS-ISAC's membership dropped from 18,574 to 5,618, a loss of about 70%. Although the organization has tried to retain members through discounts and subsidies, emphasizing that data quality remains unaffected, experts warn that vulnerabilities in local critical infrastructure may increase, while federal-level support is also shrinking.
The cyber insurance market is undergoing profound changes: insurers, in response to profitability pressures, are strengthening security controls and claims reviews for insured enterprises; the protection gap for small and medium-sized enterprises is enormous; geopolitical conflicts and the development of AI technology further exacerbate the uncertainty of risks.
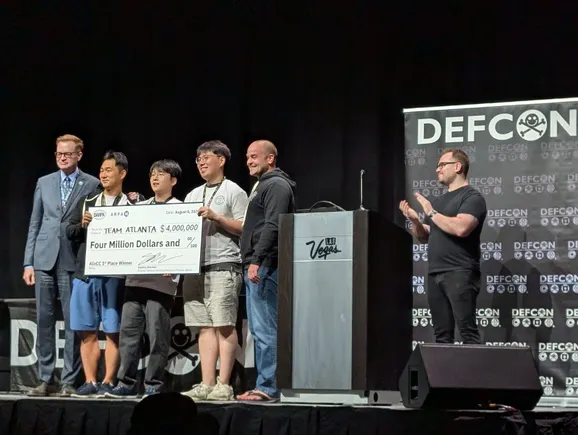
Open source AI tools born from DARPA's AI Cyber Challenge are revolutionizing vulnerability discovery at lower cost, but adoption in critical infrastructure still faces barriers.
Some U.S. critical infrastructure operators have lost confidence in the federal government's support capabilities. Led by giants such as JPMorgan Chase, Mastercard, and AT&T, the Critical Infrastructure Alliance (ACI) was established in February to promote cross-industry cybersecurity risk collaboration. Alliance Chairman Ben Flatgard stated that the private sector must proactively take on risk management responsibilities. Experts believe this move helps fill the gap left by government coordination, but the lack of federal intelligence support and antitrust exemptions remains a challenge.
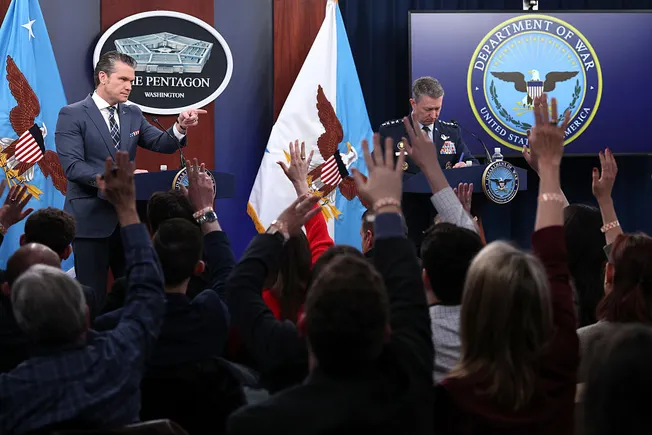
Iran has long been viewed as a persistent cyber threat to the United States, but since the escalation of the conflict between the two countries in February of this year, its tactics have significantly improved. Security research institutions point out that Iranian-backed hacker groups—including state-sponsored actors, pro-Iranian hacktivists, and economically motivated hackers—have evolved in both motivation and capability, with attacks becoming more destructive and demonstrating stronger evasion of detection. Recent cases include malware targeting Israeli water facilities, a wiper attack on medical device manufacturer Stryker, and ongoing intrusion attempts against US critical infrastructure.
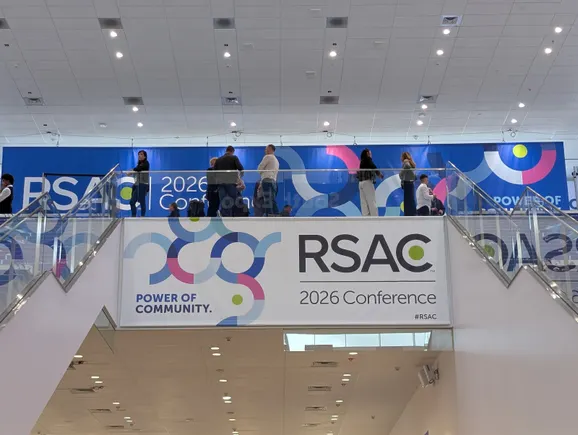
The 2026 RSAC conference took place from March 23 to 26, but U.S. government officials were absent for the first time. Previously, due to the conference organizers appointing former CISA Director Jen Easterly as CEO, the Trump administration canceled plans for officials from the White House, CISA, FBI, and NSA to attend. Multiple former government officials and industry leaders described the move as a 'missed opportunity' and an 'unforced error,' weakening collaboration between the government and the private sector in cybersecurity and the policy feedback mechanism.
Microsoft is collaborating with multiple security vendors to advance the Windows Resiliency Initiative, which aims to refactor how third-party security software operates within the Windows kernel to reduce risks similar to the CrowdStrike incident. The project is still in its early stages, involving complex work such as API redesign and feature migration, and is expected to proceed over the long term.
In 2025, the cybersecurity industry faced historic pressures: AI tools reshaped work methods while introducing new risks, and cybercrime tactics continued to escalate. Looking ahead to 2026, AI governance and guardrails, regulatory policy adjustments, a new phase in cyber insurance, patching challenges following the CVE project crisis, and operational resilience will become the five core trends. Based on expert interviews and the latest reports, this article provides an in-depth analysis of the specific impacts of these trends on enterprises.